Security Providers
Connect and manage security platforms through a single provider-neutral control plane.

THE KANGL PLATFORM
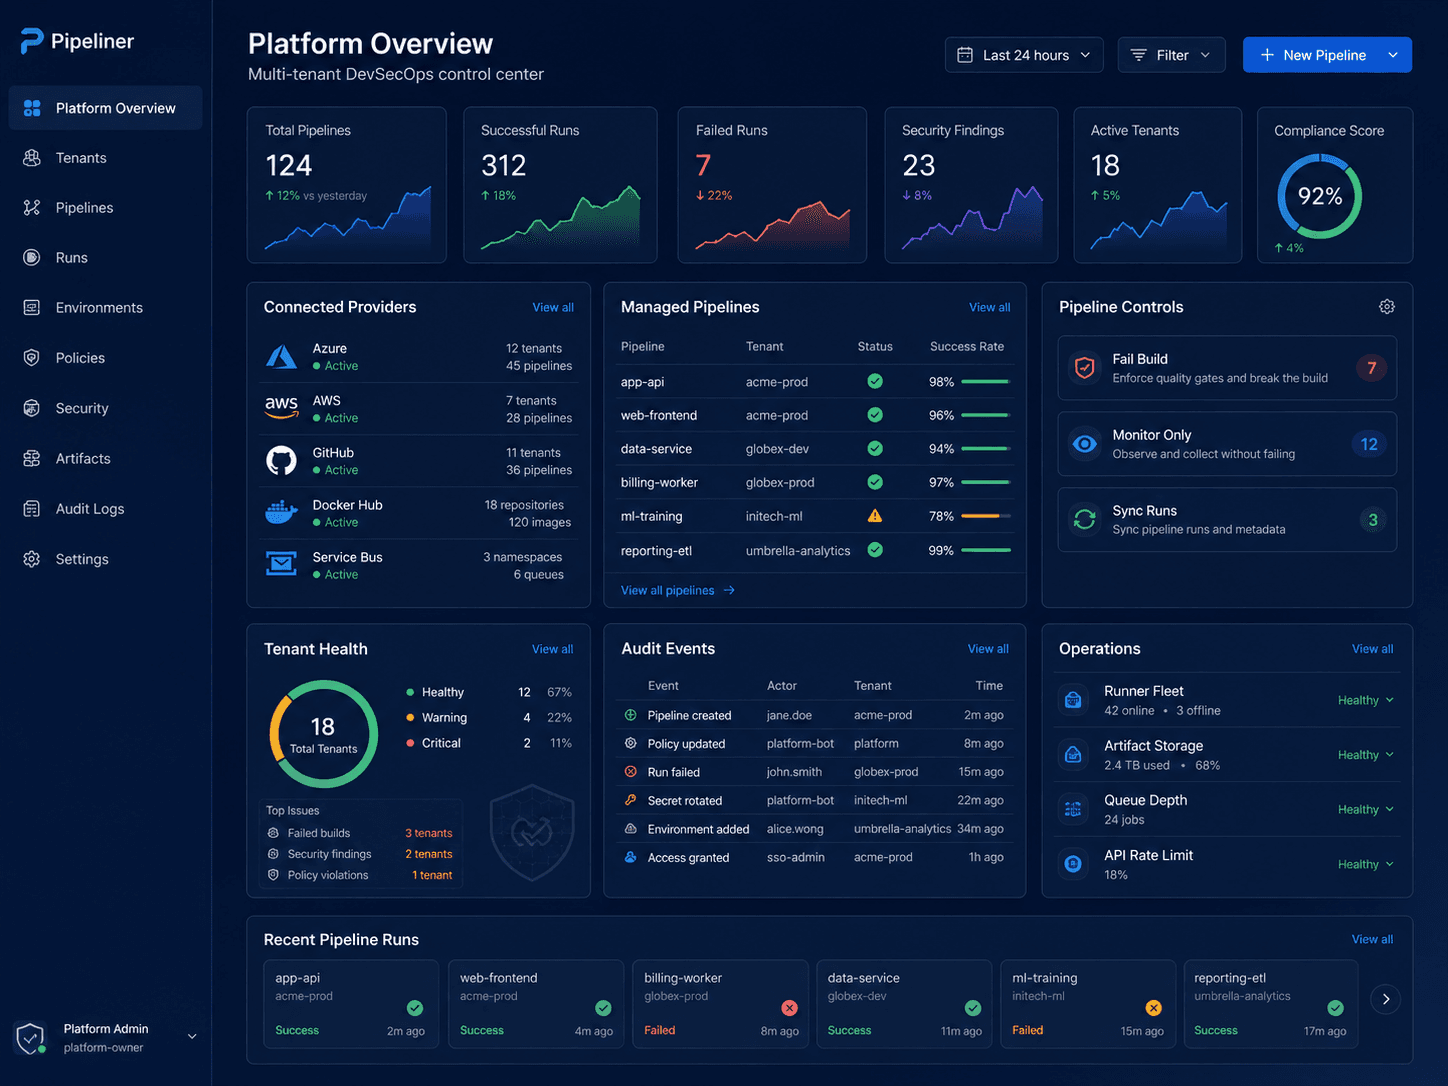
Unify provider operations, Azure DevOps build-pipeline controls, normalized posture, policy, and audit without replacing the security tools you trust.
THE COMMAND CENTER
Move from scattered vendor portals and project-by-project settings to a consistent view across the estate.
CORE CAPABILITIES
Connect and manage security platforms through a single provider-neutral control plane.
Normalize security findings into fast, consistent repository-level posture.
Enable, synchronize, and enforce controls across Azure DevOps build pipelines.
Apply backend-authoritative policy and retain durable operational history.
Map provider organizations and maintain project provisioning state.
Coordinate validation, synchronization, repair, and bulk control.
Retain durable history for provider, credential, pipeline, and policy changes.
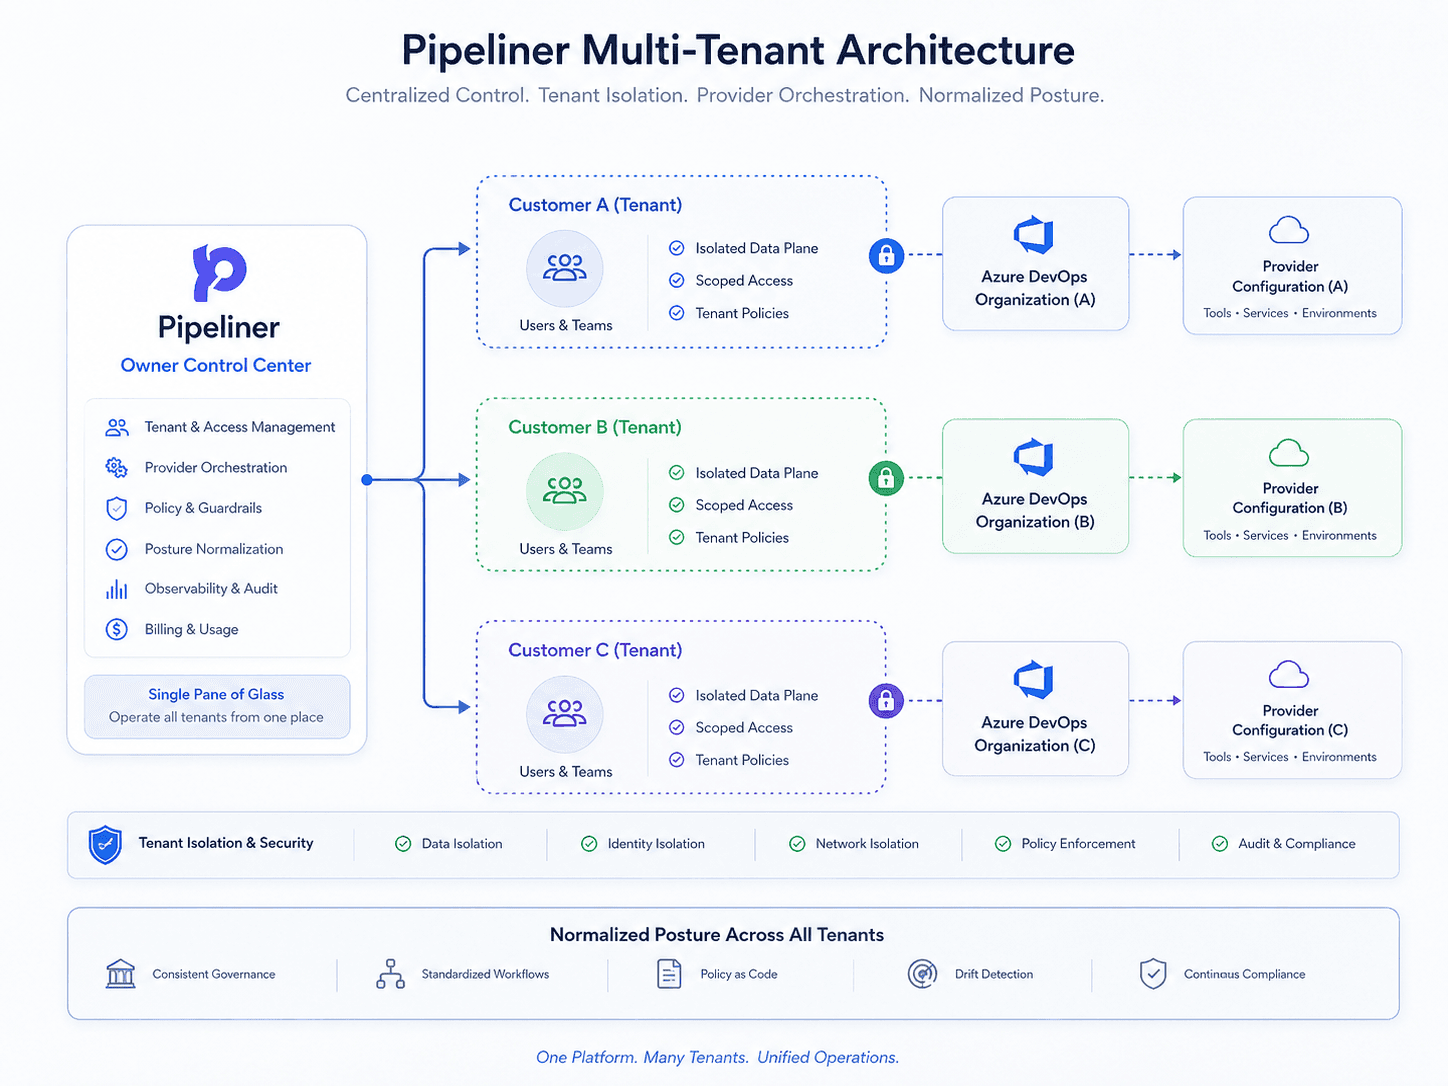
Preserve tenant configuration and provider isolation under centralized ownership.
OPERATING GUARANTEES
These are behaviors of the platform, not aspirations: how Kangl acts when providers lag, targets vanish, runs collide, or two workspaces meet one Azure DevOps organization.
Enrollment establishes the exact provider organization and repository target — and every later assessment, refresh, and repair follows that identity. Name matching survives only for repositories that were never bound, and every such fallback is logged.
A vanished provider target on a healthy connection re-enters the enrollment lifecycle automatically. Historical successes never suppress a fresh reconciliation, and concurrent observers converge on exactly one repair — never duplicate imports, never phantom runs.
Initial assessments defer with backoff inside a bounded window while the provider indexes. An exhausted window pauses as retryable instead of failing the repository; a retry restarts a fresh window. Progress is monotonic — a late exception never un-completes finished stages.
Attention items are deduplicated by canonical condition and always carry the exact remediation — repair the connection, restore the organization, choose a mapping. System-retryable states pause and retry; they never masquerade as customer actions.
Azure configuration writes require an explicit control claim, and exactly one workspace holds it per organization. Every other workspace runs observe-only, live Azure mutations fence release, and migration readiness makes workspace cutover an explicit, auditable step.
A finished setup is a durable result, not a transient screen: reloads and polls return the same completed state with the same run identity. Only an explicit “Modify setup” opens a new editing pass — a passive read never resets your progress.
ENTERPRISE ARCHITECTURE
Operate multiple customers or business tenants, multiple Azure DevOps organizations, and isolated provider configurations through one normalized control model.

SECURITY OPERATIONS, UNIFIED
Start with seven days of full plan access — or see it live with our team first.